A Linux server can appear to work normally while still hiding security weaknesses. An unused port, outdated software, or an account with excessive privileges can remain unnoticed until a security incident occurs.
Businesses often rely on Linux servers to host websites, applications, databases, and email services. A security issue can therefore affect both service availability and customer data.
Linux server security is not just about installing security software. It requires understanding what runs on the server, limiting access to resources, and ensuring existing security controls continue to work as expected.
This guide covers Linux server security best practices and solutions, including commands administrators can use to review configurations and identify potential risks.
At Bobcares, our Linux Server Management services can help businesses monitor, secure, maintain, and manage Linux server environments.
What Is Linux Server Security?
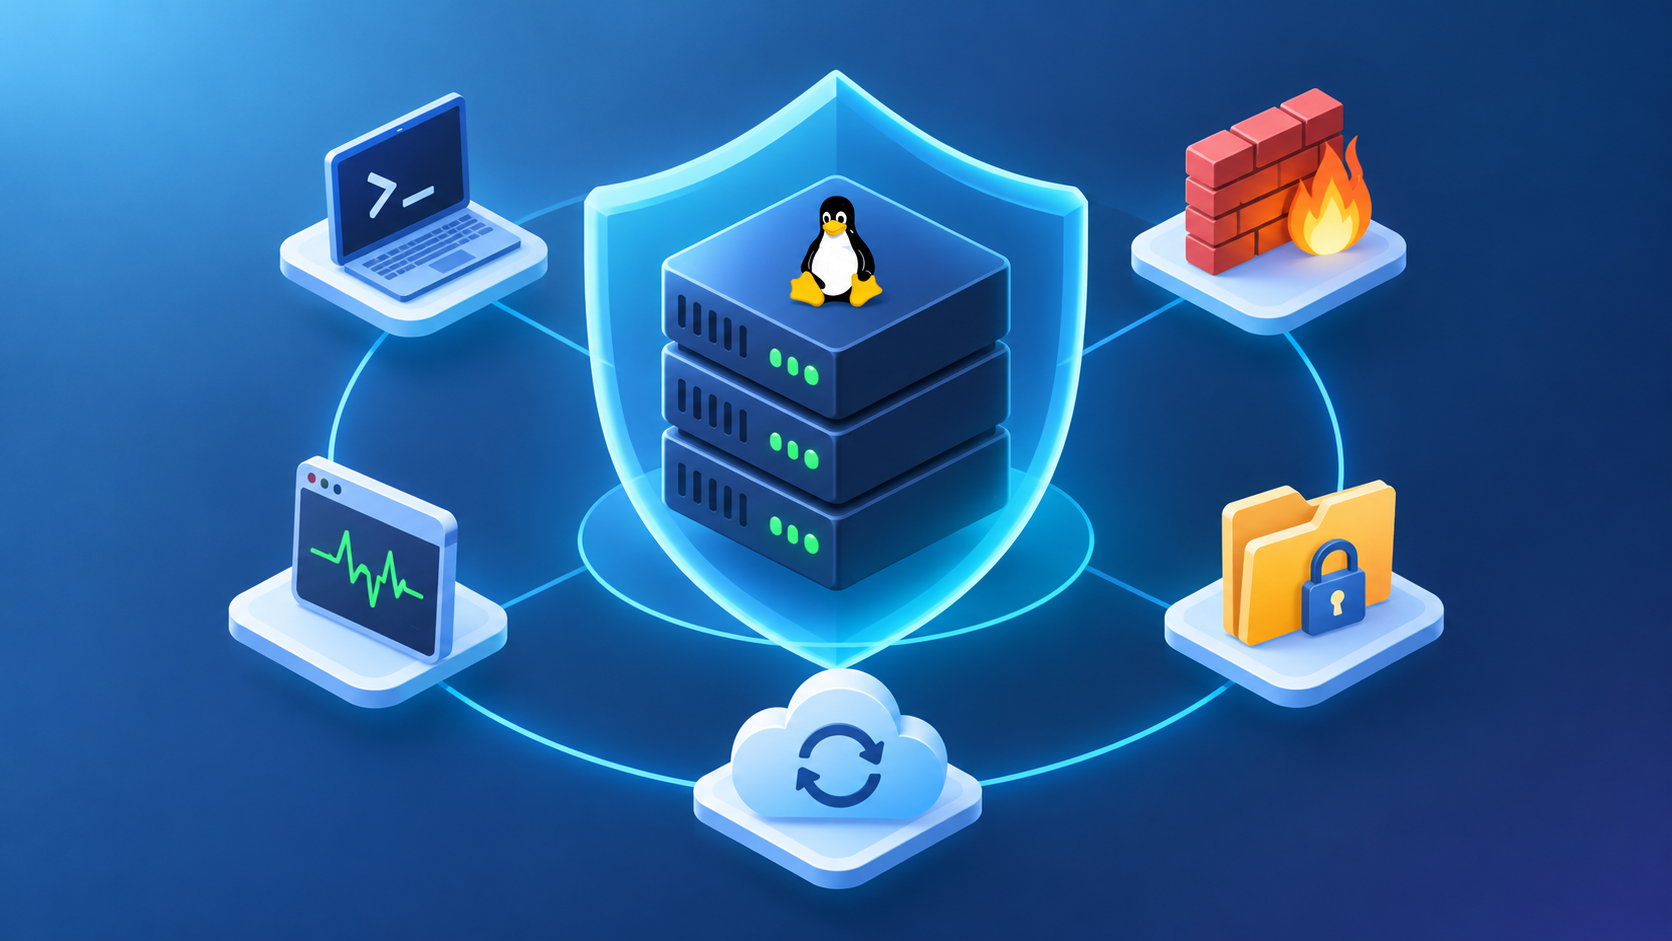
Linux server security includes the settings, tools, and practices used to protect a Linux system from unauthorized access, malware, data exposure, and service disruptions.
These measures include keeping the operating system updated, reviewing login activity, controlling network connections, managing file permissions, protecting applications, and maintaining data recovery options.
Security controls must also work together. A firewall can prevent unwanted access to a database, but weak database credentials can still create another path for unauthorized access.
Security requirements also depend on the server’s role. An internet-facing web server has different requirements than a database server that should accept connections only from an application server.
Why Is Linux Server Security Important?
Linux servers are widely used for web hosting, cloud infrastructure, enterprise applications, and database services. These systems often handle important information and provide services that customers expect to remain available.
A compromised Linux server can lead to several problems:
- Attackers may gain access through stolen credentials or weak authentication.
- Incorrect permissions or unsafe application settings can expose files and databases.
- Malicious processes or resource exhaustion can affect website and application availability.
- Unauthorized software can consume system resources and provide attackers with continued access.
- Investigating incidents, restoring data, and fixing the underlying weakness can require significant time.
No single configuration can eliminate every security threat. Regular reviews are necessary because software, users, and application requirements change over time.
Common Security Risks on Linux Servers
Administrators need to understand where security problems are likely to occur before applying security controls.
- Older kernels, web servers, PHP versions, and other packages may contain publicly known vulnerabilities. Delayed updates can leave systems exposed even after fixes become available.
- SSH, databases, development tools, and administration interfaces may be accessible from networks that do not require access. Review and close unnecessary ports and services.
- Shared passwords, unrestricted root access, unused accounts, and poorly managed SSH keys can make unauthorized access easier.
- Files that are writable by unintended users can be modified or abused. This is particularly important for website files, configuration files, and application data.
- Administrators may miss repeated login failures, unexpected processes, or file changes if they don’t review logs and system activity regularly.
Linux Server Security Best Practices
1. Keep the Operating System and Software Updated
Security patches address known vulnerabilities in operating systems and installed software. Delaying updates can leave a server exposed even when a fix is already available.
Ubuntu and Debian systems can update the package list and install available upgrades using:
sudo apt updatesudo apt upgradeAlmaLinux, Rocky Linux, and other RHEL-based systems can use:
sudo dnf check-updatesudo dnf upgradeReview production updates before installation. Check which packages will change, confirm that backups are available, and determine if services need to be restarted or the server rebooted. Testing updates on a staging system can also help identify compatibility issues.
Automation can help keep updates consistent, but administrators still need to verify that updates were applied correctly and that services continue to work as expected.
2. Harden SSH Access
SSH provides remote access to Linux servers and is an important part of server security. Public-facing systems should not rely only on passwords or unrestricted administrative access.
The SSH configuration file is located at
/etc/ssh/sshd_configPubkeyAuthentication yesPermitRootLogin noPasswordAuthentication noThese settings should only be changed after confirming that administrators can access the server using SSH keys and that another access method is available.
Check the SSH configuration before reloading the service:
sudo sshd -tsudo systemctl reload sshdSome Linux distributions use
sshsshdChanging the SSH port can reduce random scans, but it does not replace authentication and access controls.
3. Configure a Firewall and Close Unnecessary Ports
A firewall controls which network connections can reach the server. Expose only the services that need to be accessible.
Ubuntu UFW can manage firewall rules. A web server may require rules such as:
sudo ufw allow OpenSSHsudo ufw allow 80/tcpsudo ufw allow 443/tcpsudo ufw status verboseReview existing rules before changing the firewall, especially when working remotely. Incorrect rules can interrupt SSH access or customer-facing services.
Listening network sockets can be checked using:
sudo ss -tulpnReview each listening service to confirm why it needs network access. Cloud security groups and other network-level controls should also be reviewed alongside the host firewall.
4. Apply the Principle of Least Privilege
Each account should have only the permissions required for its assigned tasks. This can limit the impact of a compromised account.
Administrators can use “sudo” for approved tasks instead of sharing the root password. Review privileged groups regularly, and remove accounts that are no longer required.
File permissions also require careful attention. Wide permissions such as 777 may appear to resolve application errors, but they can allow unintended users or processes to modify files.
Check website permissions using:
ls -l /var/www/To identify files writable by all users:
find /var/www -type f -perm -0002 -printReview results before making changes, as some applications require specific permission settings.
5. Monitor Logs and Suspicious Activity
Linux logs can help administrators identify repeated login failures, unexpected service restarts, and other unusual activity.
Systems using systemd can show warning-level messages with:
sudo journalctl -p warningSSH-related activity from the previous 24 hours can be reviewed using:
sudo journalctl -u ssh --since "24 hours ago"The service name may be
sshdssh/var/log/auth.log/var/log/secureA single failed login may not indicate a problem. Repeated attempts across accounts, unusual successful logins, or changes to privileged accounts deserve closer investigation.
Centralized logging can also help administrators review events across multiple servers and alert on important activity.
6. Use SELinux or AppArmor
Linux access controls can restrict what applications and processes can do, even if a process is compromised.
SELinux is commonly found on RHEL-based distributions, while AppArmor is commonly used on Ubuntu.
Check SELinux status using:
getenforceAppArmor profiles can be reviewed using:
sudo aa-statusDon’t disable security controls just because an application hits a permission issue. Administrators should review the relevant logs and adjust policies carefully when a legitimate change is required.
7. Protect Backups and Test Recovery
Backups help restore websites, databases, configuration files, and other important data after accidental deletion, hardware failure, or a security incident.
Keep backup copies away from the server where possible, and restrict access to backup storage. Immutable copies or offline copies can provide additional protection.
A successful backup job does not guarantee that the data can be restored. Administrators should regularly test file and database recovery in a safe environment and verify that the restored data is usable.
Document recovery steps, including where backups are stored and who can use them.
8. Review Services and Remove Unnecessary Software
Every additional service creates configuration and maintenance requirements. Unused services can also create additional security risks.
Currently running services can be listed using:
systemctl --type=service --state=runningInvestigate unknown or unnecessary services before stopping or removing them, especially on servers running hosting control panels or business applications.
Also review installed packages, scheduled tasks, and externally accessible tools regularly.
Tools That Help Secure Linux Servers
| Tool | Main purpose |
|---|---|
| UFW, firewalld, nftables | Control network traffic |
| Fail2ban | Temporarily block sources that trigger configured abuse rules |
| SELinux, AppArmor | Enforce application and process access restrictions |
| auditd | Record selected security-relevant system events |
| AIDE | Detect changes to monitored files |
| Central logging and monitoring tools | Collect events and generate alerts |
These tools support specific parts of a Linux security strategy. Installing them without reviewing their configuration, alerts, and maintenance requirements does not automatically make a server secure.
Common Linux Server Security Mistakes to Avoid
Some security problems come from everyday administrative shortcuts. Common mistakes include:
- Giving broad file permissions to fix an application error.
- Keeping accounts active after they are no longer needed.
- Exposing database ports to the public internet without proper review.
- Installing updates without checking compatibility or recovery options.
- Assuming a completed backup job means the data can be restored.
- Ignoring warning messages because there are too many alerts.
- Disabling security controls instead of investigating why they are triggering.
Regular checks of users, open ports, installed software, file permissions, and backup health can help identify these issues before they become serious problems.
Frequently Asked Questions
How often should Linux servers be updated?
Review security advisories regularly, and apply updates based on the issue’s severity and the server’s exposure. Important security issues may require immediate attention, while other updates can follow a planned maintenance schedule.
Is changing the SSH port enough to secure a Linux server?
No. Changing the port can reduce automated scans, but it does not prevent unauthorized access on its own. Authentication, access controls, software updates, and log monitoring remain important.
Which Linux distribution is the most secure?
Security does not depend only on the distribution. A supported operating system that receives regular updates, uses access controls, and is actively monitored is generally preferable to an unsupported system that is not properly maintained.
Can a firewall stop every attack?
No. A firewall controls network traffic but cannot address every type of attack. It does not fix application vulnerabilities, stolen credentials, or threats that use connections the firewall already allows.
Conclusion
Linux server security depends on how a system is configured, maintained, monitored, and recovered when something goes wrong. Keeping software updated, securing SSH, controlling network access, applying appropriate permissions, and reviewing logs provide a strong foundation for server security.
Administrators should also protect and test backups, use the operating system’s security controls, and remove services that are no longer needed. Security requirements can differ between web servers, database servers, and application servers, so reviews should reflect how each system is used.
The goal is not simply to install security tools. Effective Linux server security requires understanding how exposed the system is, limiting unnecessary access, and regularly checking that the security measures in place continue to work as intended.